
Cybersecurity for Finance, When AI Reaches the Ledger
Putting AI on your financial systems does not remove a control problem. It adds one. Here are the security properties that decide whether an AI layer is safe to run on the ledger, and how ChatFin is built for each.

- An AI assistant that can read and write your ledger is a new attack surface, not just a productivity tool. The security bar in finance is higher than anywhere else in the business.
- Five properties decide whether that layer is safe to run: data protection, access that mirrors your ERP, write-back a person signs, an audit trail that holds up, and controls that get stronger, not weaker.
- ChatFin's stated posture covers each: AES-256 at rest, TLS 1.3 in transit, SOC 2 Type II, isolated tenants, US and EU data residency, RBAC, MFA, and SSO, with every agent action matched to the connected user's existing security profile.
- The layer connects through your existing systems rather than around them, drafts work for a named person to approve, and logs who ran what, what changed, and what was approved. That is a security design, not a feature list.
Putting AI on your financial systems does not remove a control problem. It adds one. The useful question is not whether an assistant can read your general ledger. It is what happens the moment it can write to it, what data leaves your boundary to get an answer, and whether every action it takes can be traced back to a person. Finance is where money moves and where auditors look, so the security bar for an AI layer here is higher than anywhere else in the company.
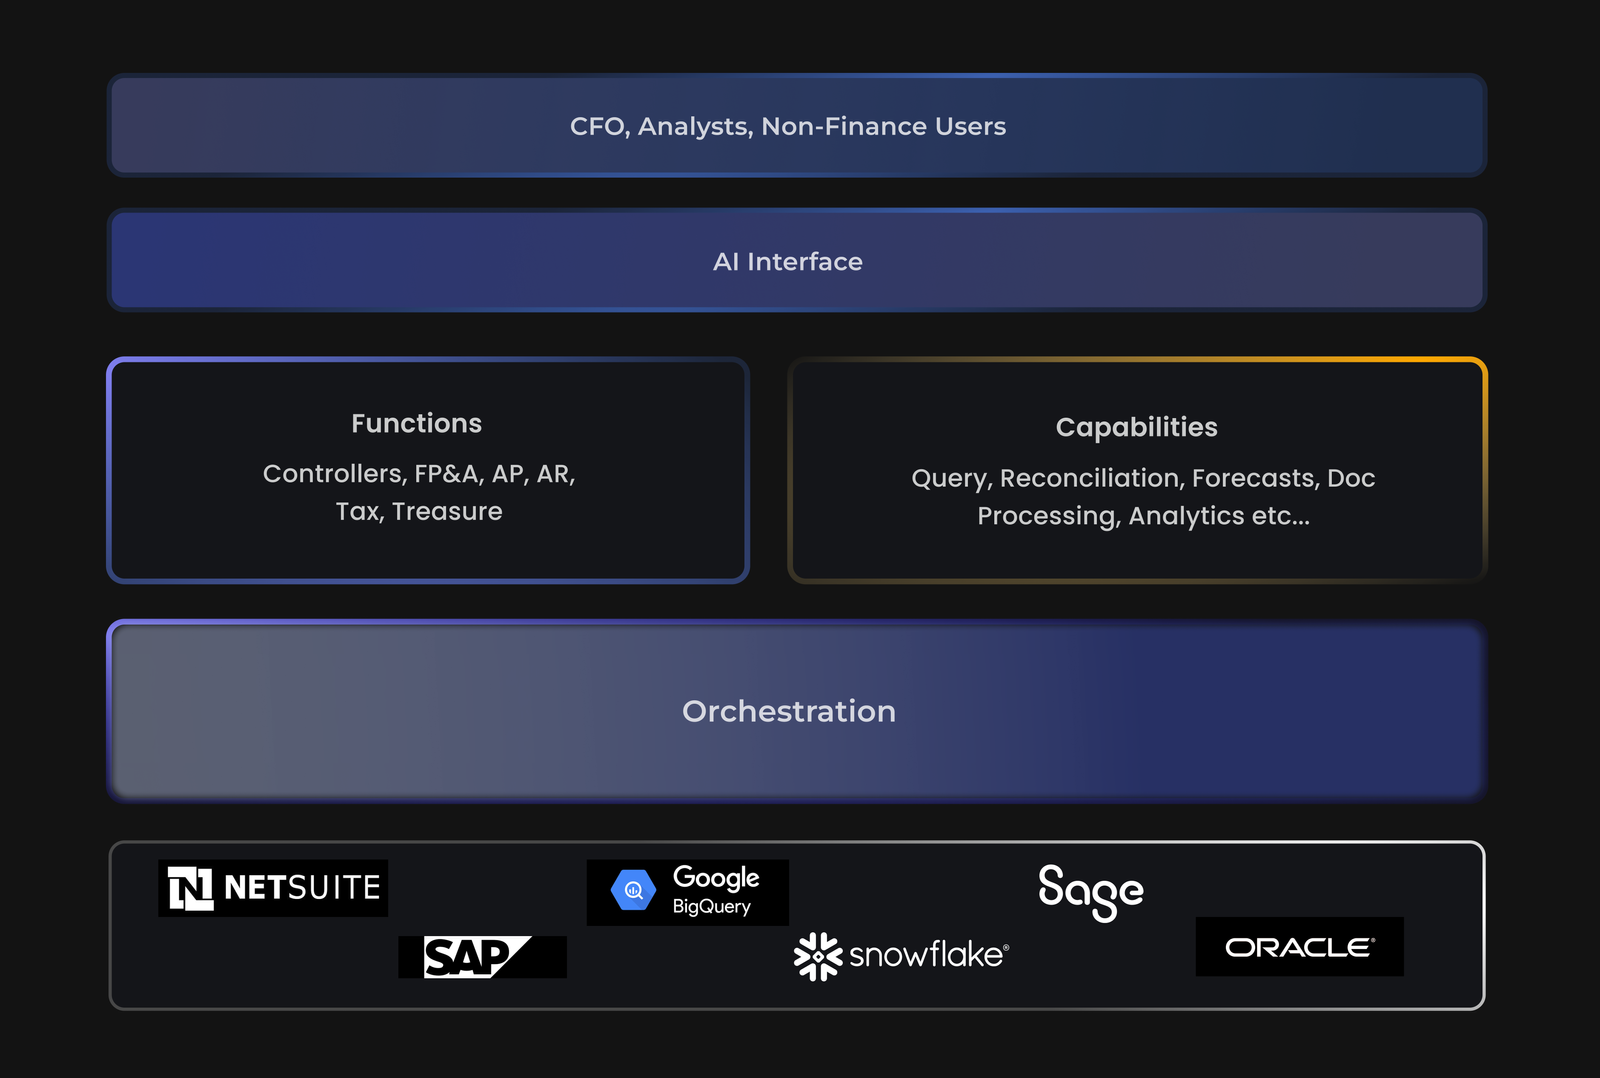
The pattern that holds up is a layer that connects through your existing systems rather than around them, mirrors the access model you already run, drafts work for a person to approve, and logs everything it does. ChatFin runs as that governed layer on top of the ERP, and the sections below walk through the five security properties that matter, and how it is built for each.
The new attack surface
Before the security posture, the threat. AI changes what can go wrong in finance in four concrete ways, and most of them are self-inflicted rather than external.
The answer is not to keep AI away from finance. It is to give it a governed path in, so the four risks above are closed by design rather than by policy memo.

Data protection, built in rather than bolted on
The first question a security team asks is where the data goes and how it is held. The answers should be boring, specific, and certifiable, not reassuring adjectives.
ChatFin's posture
Data is encrypted with AES-256 at rest and TLS 1.3 in transit. The platform is SOC 2 Type II, runs on isolated tenants so one customer's data is never commingled with another's, and offers data residency in both the US and the EU. Dedicated infrastructure is available for enterprises that require hard data isolation. None of this is a differentiator on its own. It is the price of admission, and any AI layer touching finance that cannot state it plainly should not be near the ledger.
The question is not whether AI can read your ledger. It is whether every action it takes can be traced back to a person who signed it.
Ashok ManthenaAccess that mirrors your ERP, not around it
The most common way AI becomes a liability in finance is by becoming a side door. An assistant that reads and writes with its own broad service account bypasses the permissions your ERP already enforces, and the person who could see everything through the chatbot could never see it through the application.
How it holds
ChatFin adds RBAC, MFA, and SSO on its own surface, and, more importantly, mirrors your existing ERP security model underneath. Every agent action is matched to the connected user's security profile, so an agent can only reach data that user is already authorized to view. Nothing touches the ERP without passing through authentication, validation, and permissions first. On JD Edwards, for example, this runs through Application Interface Services with role-based enforcement; the same principle applies across NetSuite, SAP, Acumatica, and the rest. The AI does not get to see more than the human it acts for.
Write-back that a person signs
Reading is low risk. Writing is where the exposure lives, and it is where an ungoverned assistant does the most damage. The safe design keeps a human between the agent and the ledger for anything that changes a number.
How it holds
Journal entries are drafted, not posted. Every transaction goes through an approval workflow before it lands, so the agent prepares the work and a named person approves it, and the two are never the same actor. Write-back runs through official interfaces, meaning native APIs and Orchestrator on JDE, never a direct write to an underlying table. Exceptions are flagged, not hidden. The effect is that segregation of duties survives the arrival of AI instead of dissolving into it.

An audit trail that stands up
A control you cannot prove is not a control. When an agent acts on financial data, the record of what it did has to satisfy an external auditor, not just an internal dashboard.
How it holds
Every action is logged: who ran it, what changed, and what was approved. Access is logged too, down to which agent read which data on behalf of which user, which is exactly what a SOC 2 or GDPR review asks you to demonstrate. Financial logic is versioned, so a change to how a metric is defined records who changed it, when, and why, and a historical report can be regenerated on the logic that was live at the time. Because answers are grounded on your ledger and master data rather than generated, every figure traces back to source, so the model reports rather than guesses. The ERP connectors are open source, so a security team can read the code instead of trusting a black box.

Controls that get stronger, not weaker
The bar for an AI layer in finance is that it should not weaken the control environment. The better outcome is that it strengthens it, by watching more of the ledger than a sampling-based process ever could.
How it holds
Continuous controls monitoring at the transaction level moves SOX and ICFR work from periodic sampling toward closer-to-real-time assurance. Anomaly detection flags entries that do not fit the pattern, and duplicate or erroneous payments are caught before the money leaves rather than chased weeks later. This is the same discipline behind fraud and audit controls, applied continuously rather than at quarter-end.
One boundary worth stating plainly. ChatFin is not a firewall, a SIEM, or an endpoint tool, and it does not replace your security stack. It secures the finance-AI layer and hardens the financial controls that sit on top of your ERP. The distance between a general assistant that can touch finance and a system built to stand behind what it touches is the same distance between a generalist copilot and a specialist finance system, and in security terms that distance is the whole point.

Security is a design choice, not a disclaimer.
ChatFin connects to your ERP through native interfaces, mirrors the access model you already run, drafts work for a named person to approve, and writes back through supported APIs with the trail intact. The posture behind it is stated, not implied: AES-256 at rest, TLS 1.3 in transit, SOC 2 Type II, isolated tenants, and data residency in the US and EU, with open-source connectors your team can audit.
Because the layer is grounded on your ledger, its figures are yours, traceable to source, and defensible during an audit. See the full integration coverage to check how it maps to your stack.
The goal is not to add another tool that can touch finance. It is to add a layer that can stand behind everything it touches.
Book a demoSee the security model on your own ERP and data.
We will walk through how ChatFin authenticates, what it can and cannot reach, how write-back is approved, and what the audit trail looks like. Bring your security questions and your ERP, and we will map them end to end.