
JD EDWARDS SECURITY
How to Securely Use JD Edwards Financial Data With Generative AI While Meeting Compliance and Data Residency Requirements
Some compliance obligations were deferred by sixteen months this year, and others arrived on schedule.
- Data minimisation is the strongest control available. Aggregating at source means summaries travel rather than ledger rows.
- Ledger data frequently contains personal data in supplier and customer records, which brings privacy obligations alongside commercial confidentiality.
- Under the Digital Omnibus agreed in May and confirmed by the Council in June, EU AI Act high risk obligations for Annex III systems moved from August 2026 to December 2027.
- Most transparency obligations were not deferred and applied from 2 August 2026, so treating the Act as delayed is a misreading.
- ChatFin minimises what leaves the boundary, keeps model region configurable and produces the documentation a review asks for.
Compliance conversations about AI in finance tend to be conducted at a level of abstraction that produces no decisions. The useful version is concrete: what data moves, where it goes, who retains it, and what documentation exists.
This page covers those four, plus where the regulatory timeline currently stands, with the caveat that none of it is legal advice and your own counsel should confirm how the obligations apply to you.
Minimisation Is the Control That Does the Most Work
Before considering any regulatory framework, reduce what leaves your boundary. This is the single most effective compliance measure available and it is a design decision rather than a policy one.
Because the data service supports aggregation and paging, sums and groupings can be computed inside JD Edwards so that a small correct result travels rather than thousands of ledger rows. That improves accuracy and performance as well, which makes it an easy argument internally.

Personal Data Inside the Ledger
This is regularly overlooked. Financial data is treated as a commercial confidentiality question, and supplier and customer records frequently contain names, contact details and bank information belonging to identifiable people, particularly where you deal with sole traders and small businesses.
That brings privacy obligations into scope alongside the commercial ones, and the practical implications are about purpose, retention and the ability to answer a subject request.
Provider Terms Are a Contractual Control
Whatever the architecture, the terms under which a model provider handles your content are a control in their own right, and they should be settled before deployment.
Where the EU AI Act Timeline Now Stands
This changed materially during 2026 and the change is widely misreported. Under the Digital Omnibus on AI, agreed politically in May and given final approval by the Council at the end of June, high risk obligations for standalone Annex III systems moved from 2 August 2026 to 2 December 2027, and those for high risk systems embedded in regulated products moved to 2 August 2028.
The important nuance is that most transparency obligations were not deferred and applied from 2 August 2026 as originally scheduled, with certain provider side marking requirements moved to December 2026. Reading the headline as the AI Act has been delayed is therefore a mistake with a compliance consequence.
Documentation a Review Will Ask For
Regardless of framework, the same artefacts get requested, and having them prepared turns a long review into a short one.
None of these is onerous to produce if the architecture was designed with the review in mind, and all of them are difficult to reconstruct afterwards.

Human Oversight Is Also a Compliance Answer
The approval design that exists for financial control reasons happens to answer a great deal of what a compliance review asks, which is a useful alignment.
A system where a named person reviews and approves every posting, with the evidence in front of them and the decision recorded, is straightforwardly describable as meaningful human oversight rather than nominal sign off.
"Reading the headline as the AI Act was delayed is a mistake with a compliance consequence. Some obligations moved sixteen months. Others did not move at all."

How ChatFin Approaches This
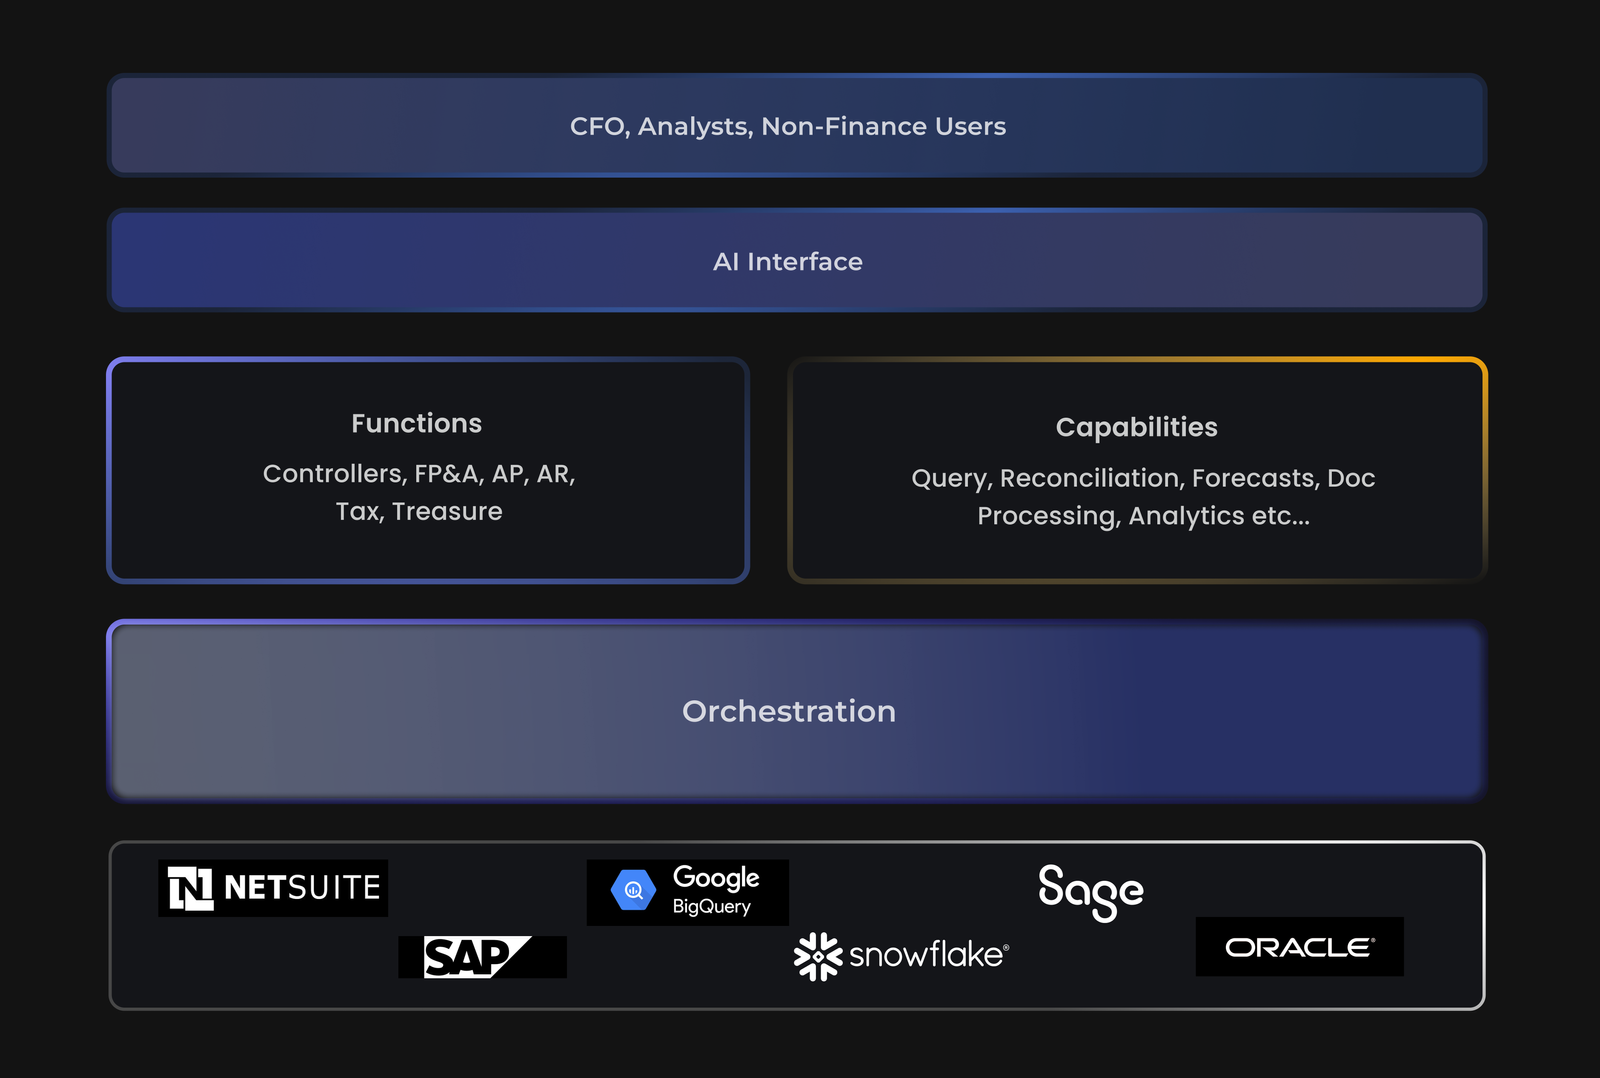
ChatFin minimises what leaves your boundary by aggregating at source, keeps model selection and region configurable so residency and handling obligations can be met, and enforces named human approval on anything that posts.
The audit record is produced automatically and is itself treated as data with a deliberate location and retention period. We are not lawyers and none of this is legal advice, so your own counsel should confirm how these obligations apply to your circumstances.

Minimise What Moves, Document What Remains
ChatFin aggregates at source so summaries travel rather than ledger rows, keeps model region and provider terms configurable, enforces meaningful human approval, and produces the documentation a compliance review asks for.
The strongest compliance control is architectural. Send less, and most of the conversation becomes shorter.
Frequently Asked Questions
What is the strongest control for using ledger data with generative AI?
Data minimisation, and it is a design decision rather than a policy one. Because the JD Edwards data service supports aggregation and paging, totals and groupings can be computed inside the ERP so a small correct result travels instead of thousands of rows. That improves accuracy and performance as well as exposure, which makes it straightforward to argue internally.
Where does the EU AI Act timeline currently stand?
It changed materially during 2026. Under the Digital Omnibus on AI, agreed politically in May and approved by the Council at the end of June, high risk obligations for standalone Annex III systems moved from 2 August 2026 to 2 December 2027, and those embedded in regulated products to 2 August 2028. Most transparency obligations were not deferred and applied from 2 August 2026, so reading the headline as a general delay is a mistake. This is not legal advice and your own counsel should confirm scope.
Does financial data count as personal data?
Parts of it frequently do, and this is regularly overlooked because financial data is treated purely as a commercial confidentiality question. Supplier and customer records often contain names, contact details and bank information belonging to identifiable people, particularly where you deal with sole traders and small businesses. That brings obligations around purpose, retention and the ability to answer a subject request, including within the audit record.